Symantec bought Vontu. Never heard of Vontu? They are an established player in the data-leakage security niche. Primarily deployed on networks that fall under the purview of the Gramm-Leach-Bliley Act, Vontu's flagship product works like an IPS, but instead of loading it up with vulnerability signatures, you load it up with keywords and snippets of your confidential data.
For $350M, this is is a gamble for Symantec for a couple of reasons. First, the expansion of the data-leakage market is very much a question-mark. Sure Vontu's poised to dominate if it does blow up, especially with Symantec's Panama Canal of a channel. But Symantec is a desktop client company. They've killed every network device they've ever acquired, and some that they built themselves. Sure Vontu has a desktop client as well, but it's not their leader.
What I find most interesting about this acquisition is that Symantec is known for paying pennies for secondary niche players and trying to pump them on their brand recognition against primary niche players. Their whole product strategy can be summed up as "one brand, one vendor." In this case, they bought one of the best-of-breed players in the niche, if not the top dog. And they paid good money for them, too. Recent acquisitions like Altiris and Revivio were more of the old Symantec trying to find a bargain buy into a new market. So the Vontu purchase leaves me confused. I would've expected Symantec to buy somebody like Tizor and stay away from Vontu and PortAuthority.
By the way, there's an excellent Forrester paper on Symantec's ongoing shopping spree. If you work for a Forrester subscriber, or own a lot of Symantec stock, it's worth reading. (I am the former and, at not the latter, for what that's worth.) If you're keeping track, Symantec has acquired no fewer than 31 companies since 2000.
Also, Vontu co-founder (and recent multimillionaire!) Joseph Ansanelli testified before a House subcommittee about combating identity fraud. (PDF Link) Another interesting read, but when you contrast this with the recent ID theft study that Bruce Schneier blogged about today, you have to wonder if there's a decent sales line for these products beyond GLBA compliance.
Wednesday, November 7, 2007


Tuesday, November 6, 2007
Am I Not In On The Joke?
So I just found Security Mike's Guide to Internet Security.
You have to understand that I respect the hell out of Mike Rothman. Which is why I am choosing to believe that this is an elaborate tongue-in-cheek joke that I'm just not able to extract the punchline from.
This quote in particular has me convinced that this is some sort of hoax:
That something is selling a 6-month website subscription for $37. So either I have just seen the Lone Ranger take a bribe and slap an old lady, or I am still not in on the joke. Mike's selling a book for the mom set on how to secure their own computer? Because paying for McAfee is some sort of injustice?
I teach a course very similar to Mike's book through my employer's corporate training program. If you would like a copy, e-mail me, and I will send you the slide deck. Steal my bullet points. Pass my advice around. I don't want any money. If you feel like giving me credit, that's cool. The people this is really for don't know who I am anyway.
Be free, common sense, be free!
I'll just leave you with this:
It conjures images of clowns and ponies and free hot dogs at a used car lot.
You have to understand that I respect the hell out of Mike Rothman. Which is why I am choosing to believe that this is an elaborate tongue-in-cheek joke that I'm just not able to extract the punchline from.
This quote in particular has me convinced that this is some sort of hoax:
"You certainly can pay your local Geek to come over and configure your computer and sell you lots of software you have no idea about. Bring your checkbook – it’s going to run you hundreds You can do it yourself of dollars. And you get to pay every year to renew your software as well. Don't forget the Geeks get paid when you buy software as well, so they have an interest in loading you up with stuff you don't need.
It’s not right. So I decided to do something about it."
That something is selling a 6-month website subscription for $37. So either I have just seen the Lone Ranger take a bribe and slap an old lady, or I am still not in on the joke. Mike's selling a book for the mom set on how to secure their own computer? Because paying for McAfee is some sort of injustice?
I teach a course very similar to Mike's book through my employer's corporate training program. If you would like a copy, e-mail me, and I will send you the slide deck. Steal my bullet points. Pass my advice around. I don't want any money. If you feel like giving me credit, that's cool. The people this is really for don't know who I am anyway.
Be free, common sense, be free!
I'll just leave you with this:
"Best of all, there is NO RISK to you. You don’t like Security Mike's Guide? Get your money back. [...] Regardless of the reason, if you are unhappy – I will send your money back. That’s right. If you aren’t happy, you can have your money back. I’ll wish you good luck because Security Mike’s Guide isn’t for everyone. It’s all good."
It conjures images of clowns and ponies and free hot dogs at a used car lot.
Monday, November 5, 2007
For the Paranoid
Been too busy to blog lately. Got a few things half-ready to post. Just need to find the time, motivation, and answers to get them posted. So this is just a proof-of-life post, I guess.
This story from Radar Mag made my day, sort of. It's an excellent story, but if you're paranoid like me, it may take you some place you'd rather not go. Maybe I should move my blog to typepad. :-)
This story from Radar Mag made my day, sort of. It's an excellent story, but if you're paranoid like me, it may take you some place you'd rather not go. Maybe I should move my blog to typepad. :-)
Friday, October 26, 2007
The Heartbreak of Nondisclosure
Look what I've got in the test lab this week:

It's a little more recognizable with the front bezel on it:

That's right, it's ArcSight Logger 2.0 beta! Alas, the non-disclosure agreement prevents me from telling you any more than that. OK, I'll also tell you that, much to my disappointment, the cool logo bezel does not light up.

It's a little more recognizable with the front bezel on it:

That's right, it's ArcSight Logger 2.0 beta! Alas, the non-disclosure agreement prevents me from telling you any more than that. OK, I'll also tell you that, much to my disappointment, the cool logo bezel does not light up.
Sunday, October 21, 2007
Addendum: If I Could Tell Your CISO 3 Things
On the issue of spending on monitoring versus prevention, I stand by what I said about spending on monitoring equal to prevention. But there's another point worth making that I missed the first time around. So, if I may, I'd like to tell your CISO another thing.
1b) Let the results of your 2007 monitoring determine what you spend your 2008 prevention dollars on. Simply put, no consultant, auditor, or magazine is going to know better than you what your security problems are. So, unless you still don't believe me about monitoring, don't let them tell you how to spend your money. (Remember that "deep packet inspection firewall" you bought in 2005? That's what you get for listening to a magazine.)
Set aside time each year to review what your big messes were as well as where your analysts spent the majority of their time. Then look at the market for technologies that can cut the amount of time your talent spends doing the same thing over and over by hand. Also look at technologies that can help you keep the promises you made under your breath to never let _____ happen again.
So while there may be no Security-ROI-Santa-Claus, comprehensive operational security is self-supporting. Leverage it to the maximum extent that you are able.
A Little Wi-Fi Hacking With Your Half-Caf Nonfat Mochachino?
So like, literally right now Vivek and Sohail from AirTight networks are presenting on a new attack on WEP at Toorcon. This new technique, cheekily dubbed Cafe Latte, attacks clients instead of access points. But according to an interview that the researchers gave prior to Toorcon, the attack can take from a few minutes to a few hours, making it no more efficient than existing techniques.
Cool research guys, but I guess the question I have is this. If I need to attack a mobile client instead of an access point in order to avoid detection by, I dunno, a wireless IDS of some sort - and I have to struggle with position and availability of the target, no less - won't I be shocked to discover that your technique works because this highly secure wireless network uses WEP?!
I'm just saying. Attacks against wireless clients in the field are interesting, and fertile ground for all sorts of cool hacks and lucrative crime. But - and maybe I'm missing the obvious here - I don't get it.
Monday, October 15, 2007
A Little YouTube Nostalgia
Nothing serious, just some computing throwbacks.
Remember when Bill Cosby sold computers? Or when Windows 1.0 came out? (Yeah, that is Steve Ballmer in the godawful jacket.) What about when Commodore 64 got a joystick? Did you even know that Atari made computers?
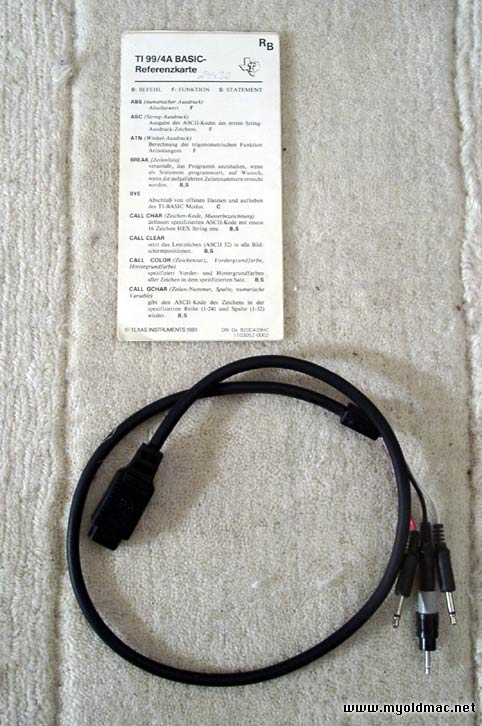
I had a TI-99/4A back in the day. With the 300bps acoustic coupler and the cassette storage cable to record my BASIC programs for later retrieval. I'm so friggin' old I could cry.

Subscribe to:
Posts (Atom)